-
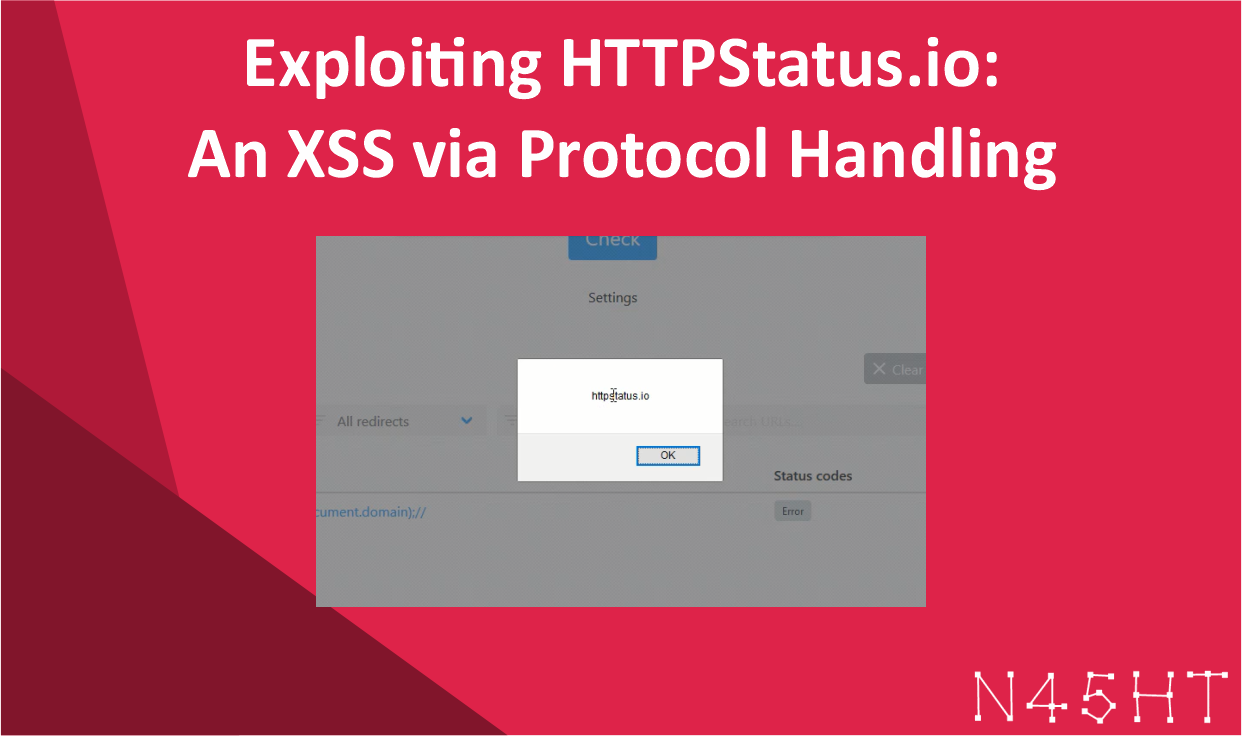
Exploiting HTTPStatus.io: An XSS via Protocol Handling
httpstatus.io is a tool that allows you to check HTTP status codes, headers, and redirects. For example, when…
-
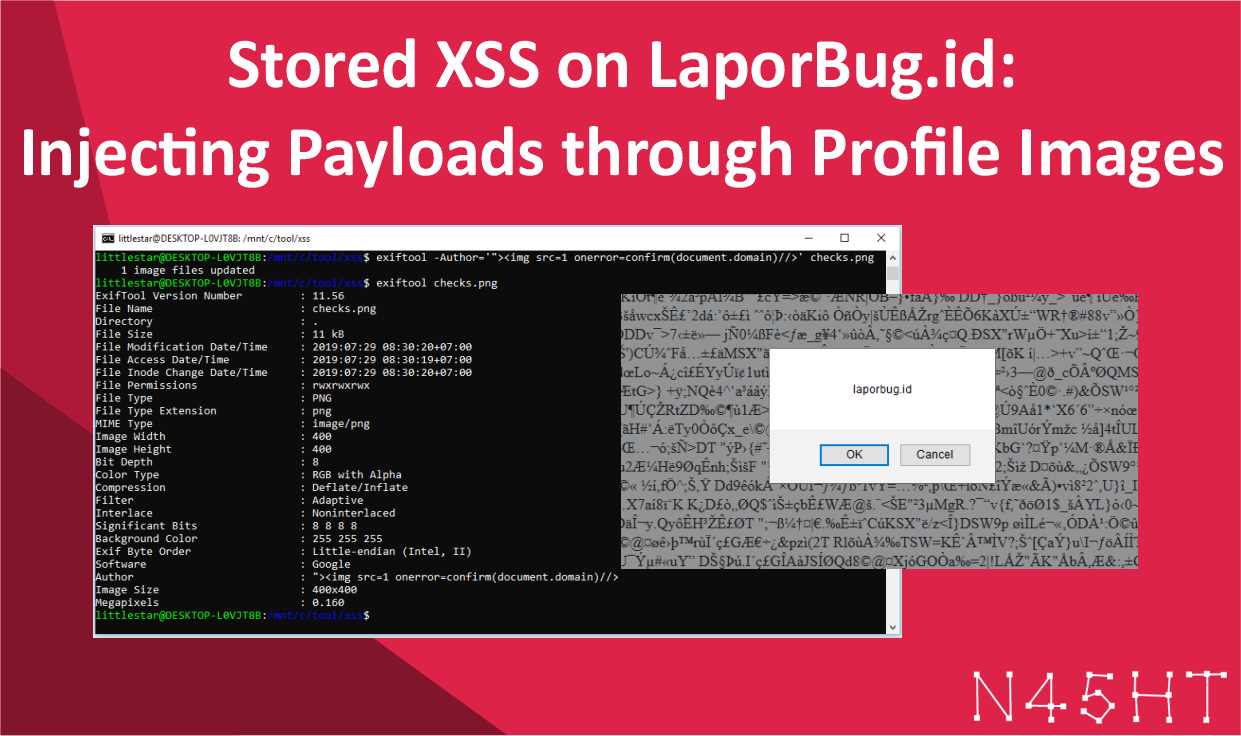
Stored XSS on LaporBug.id: Injecting Payloads through Profile Images
LaporBug.id is a Bug Bounty Platform based in Indonesia. If you want to know more about LaporBug.id, visit…
-
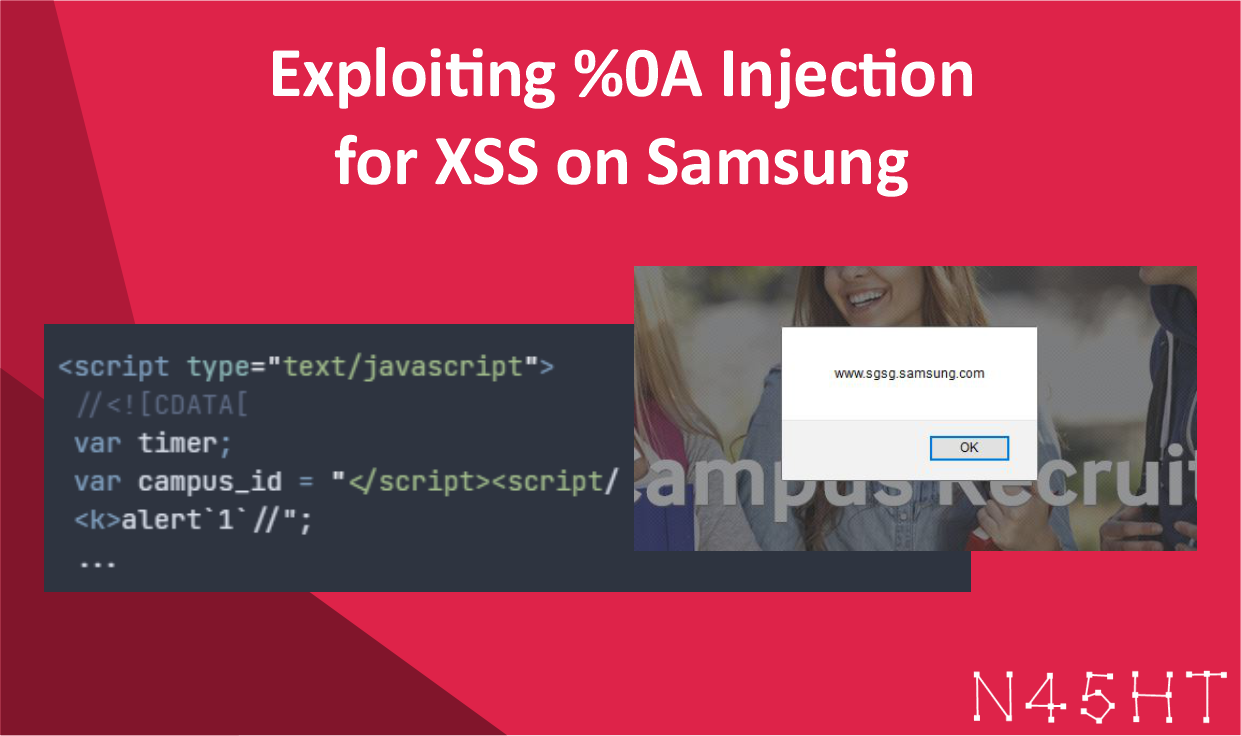
Exploiting %0A Injection for XSS on Samsung
I began by searching for subdomains using Sublist3r and then checked the HTTP status codes for each subdomain…
-
POST-based XSS on DomaiNesia
DomaiNesia is a company that offers domain registration, web hosting, VPS, and other related services. In this report,…
-
Reflected XSS Hidden Input in AT&T
During my testing of AT&T’s common login page, I discovered a reflected XSS vulnerability in the transactionID parameter.…
-
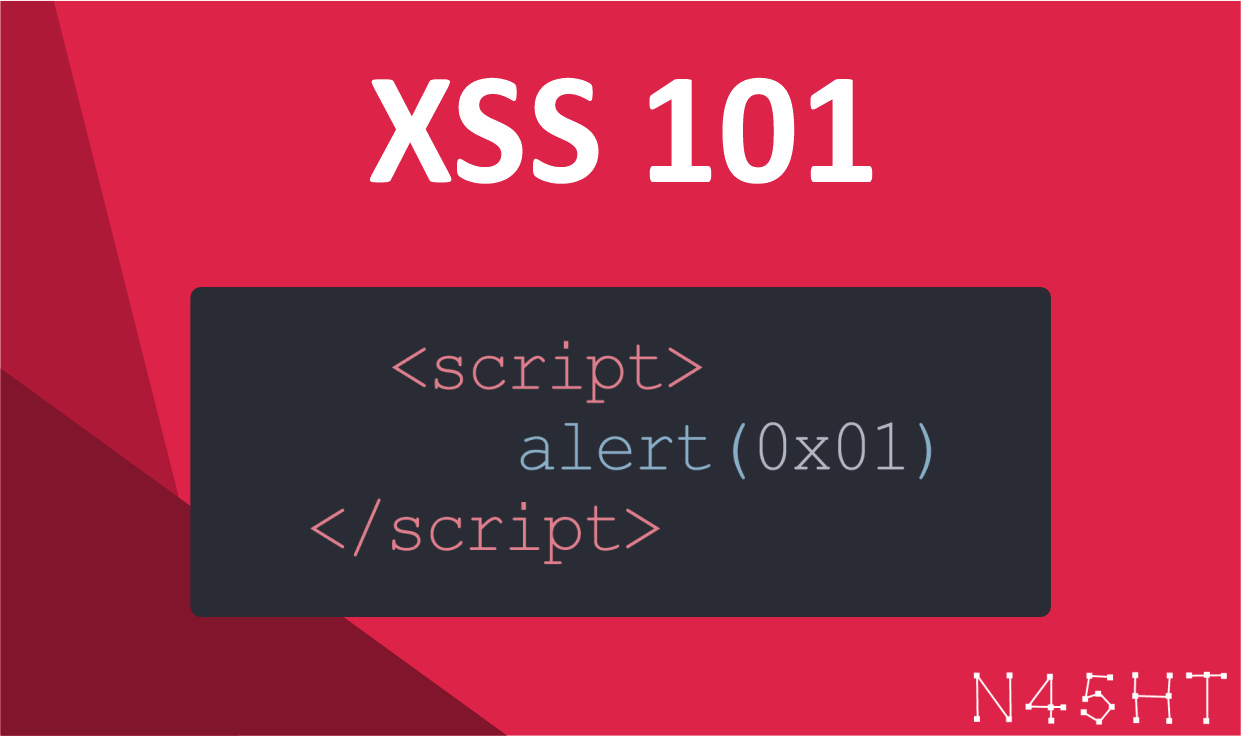
XSS 101
What is XSS? Cross-site scripting (XSS) is the most common vulnerability in web applications and allows an attacker…
-
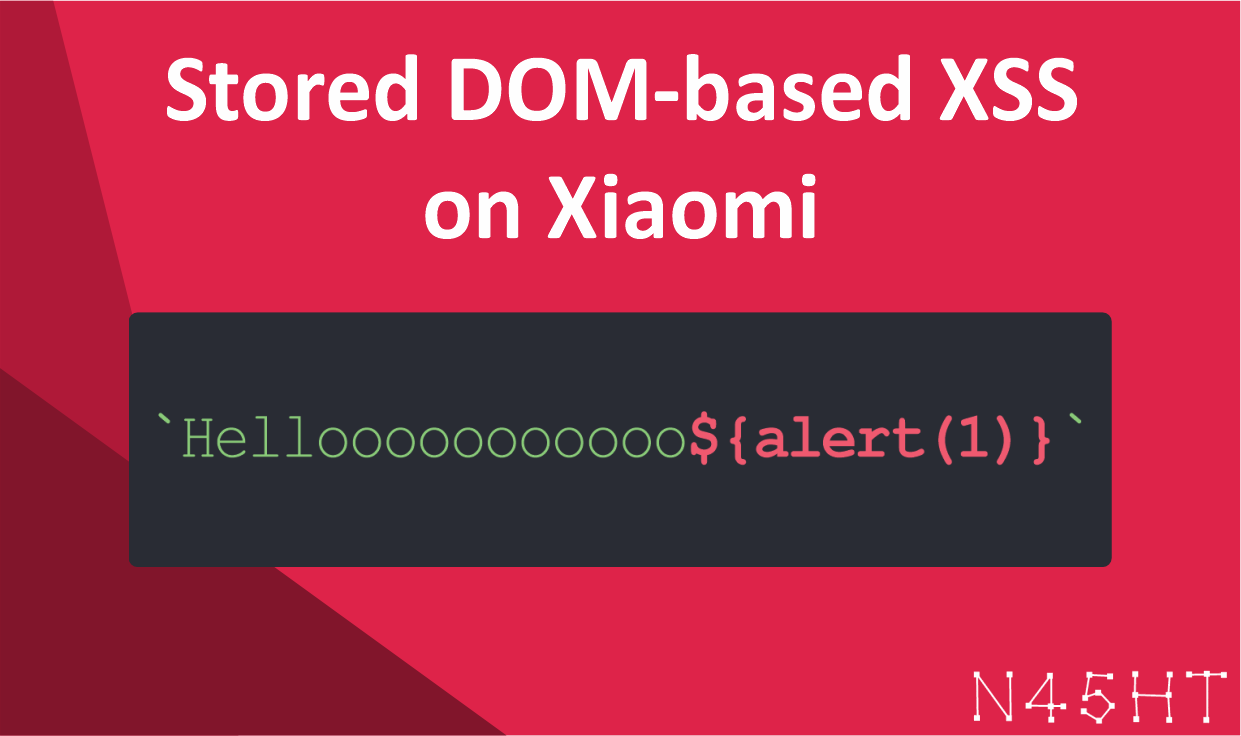
Stored DOM-based XSS on Xiaomi
Yesterday, I discovered a Stored Cross-Site Scripting (XSS) vulnerability on the Xiaomi Forum via Markdown. Today, I’ve found…
-
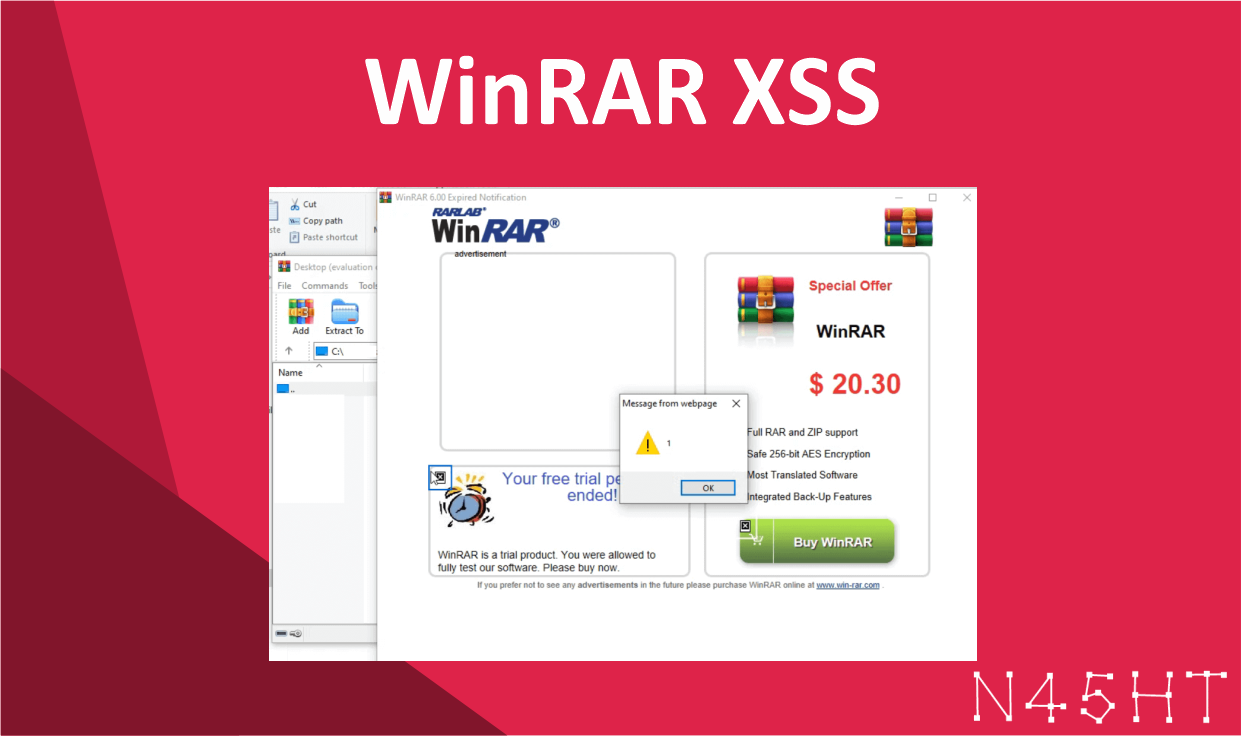
WinRAR XSS
A few days ago, I discovered a Cross-site Scripting (XSS) vulnerability in WinRAR. In this article, I’ll walk…
Recent Posts
- The CSS Backdoor Nobody Talks About
 Webmail clients like Gmail, Outlook, and Fastmail sanitize untrusted HTML/CSS… Read more: The CSS Backdoor Nobody Talks About
- Critical Analysis of CVE-2026-50522: Microsoft SharePoint Remote Code Execution Vulnerability
 Microsoft SharePoint is one of the most widely used enterprise… Read more: Critical Analysis of CVE-2026-50522: Microsoft SharePoint Remote Code Execution Vulnerability
- We’re Hiring: Python Cybersecurity Expert
 Hiring Status: Closed Applications for this position are no longer… Read more: We’re Hiring: Python Cybersecurity Expert
- XSSR Pro is Now Available for Free
 We’re excited to announce that XSSR Pro is now available… Read more: XSSR Pro is Now Available for Free
- Drupal CVE-2026-9082 Checker
 We recently created a small Python tool to detect CVE-2026-9082,… Read more: Drupal CVE-2026-9082 Checker
Social Media
Advertisement
Tags
API Bug Bounty Capture The Flag Command Injection Cross-site Scripting CSS CTF CVE-2026-9082 CVE-2026-50522 Drupal ExifTool HTML Information Disclosure JavaScript Markdown Microsoft SharePoint Open Redirection PHP SQL Injection VDP WAF Web Application Firewall XSS XSSR XSSRush